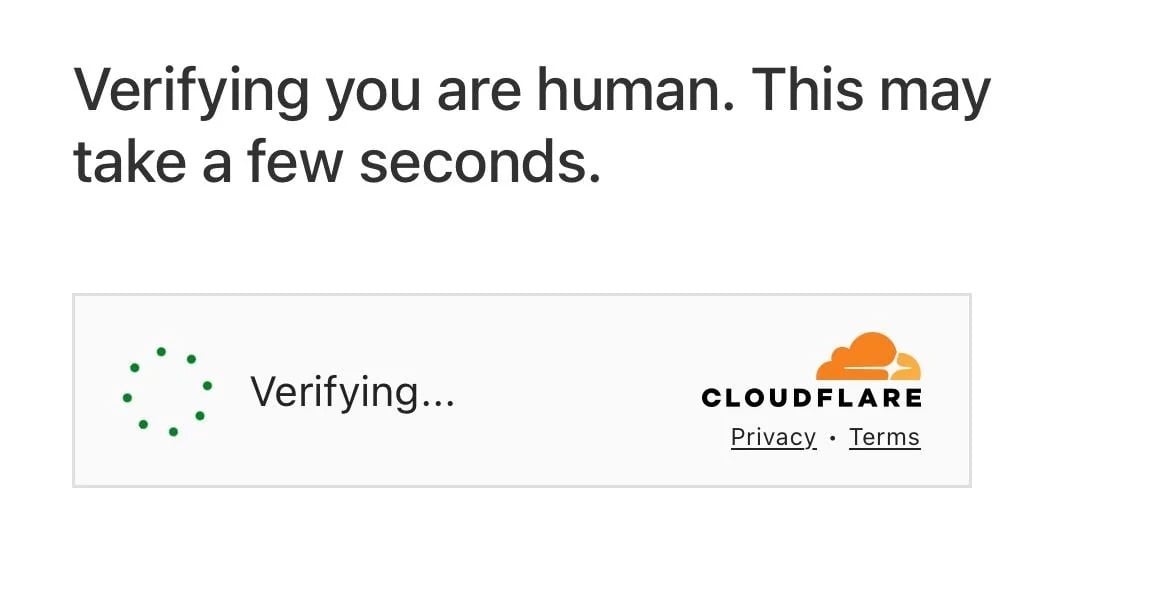


Many websites and online platforms use Cloudflare in order to properly handle web traffic. Cloudflare has become so ubiquitous that the few times the company’s services have gone down, a significant portion of the internet goes down with it.
Hackers are very aware of this and are now rolling out new cyber attacks that impersonate Cloudflare in order to trick unsuspecting internet users into giving these cyber criminals unauthorized access to their computers.
One such attack, according to reports, weaponizes Cloudflare’s verification pages, often found on websites to prove a user is human and not a bot, in a ClickFix campaign. The newly discovered attack was recently discovered by cybersecurity researchers at the SANS Technology Institute’s Internet Storm Center.
ClickFix campaigns are cyber attacks that rely on social engineering tactics. There are no software or hardware security flaws involved. There isn’t even a harmful file that a user was tricked into downloading. An unsuspecting victim is simply tricked into copying and executing malicious commands on their own device, which can download malware or provide the hacker with access.
In this specific newly discovered attack, users visit a website that has already been compromised by the hacker. After clicking the Cloudflare verification box to prove they are human, the user is told that the process is taking longer than usual. The user does not know that this Cloudflare verification box is a fake, set up by the hacker.
The prompt informs the user that to speed up the process, they need to follow the directions on the screen and run a specific command. This is where the hacker then gains access.
According to the report, a different set of instructions appears to users based on whether they access the website through a PC running Windows or a Mac. The report lists requests that appear intended to track information such as the visitor’s location and IP address.
The report states that this attack has been rolled out across multiple compromised websites.
Users should know of the ordinary verification methods, such as clicking verification boxes or completing a CAPTCHA. A user should never open up their terminal or Run box to complete a human-verification check.
Source: https://mashable.com/tech/fake-cloudflare-verification-tricks-users-into-giving-hackers-access